<img src="https://secure.leadforensics.com/97241.png" style="display:none;">

Network visibility for managed security service providers

Network Critical provides network visibility solutions for managed security service providers (MSSPs) running multi-client SOC monitoring, threat detection, and compliance capture operations.

Network teams at these organisations run Network Critical visibility

  • Vodafone Logo
  • HSBC Logo
  • bp logo
  • Airbus Logo
  • Darktrace Logo

Delivering complete network visibility across managed security operations

Managed security service providers protect dozens of client networks simultaneously, each with different link speeds, tool requirements, and compliance obligations. Network Critical's SmartNA-PortPlus scalable packet broker delivers 100% packet capture across every client environment, aggregating traffic from 48 to 194 ports at 1G to 100G to feed SIEM, NDR, and forensic capture tools without packet loss. Where MSSPs rely on SPAN ports, they inherit silent packet drops that compromise the detection fidelity their clients are paying for. A purpose-built visibility layer using network TAPs and network packet brokers eliminates that risk, reduces tool licensing costs through intelligent traffic conditioning, and scales as new clients onboard without forklift upgrades. Organisations including Darktrace and Bourne Leisure have deployed Network Critical to connect and optimise their security tool stacks.
 Key challenges facing managed security service providers 

Silent packet loss undermines detection fidelity
SOC analysts depend on complete traffic feeds to detect lateral movement and advanced persistent threats. When SPAN ports drop packets during client traffic spikes, NDR and SIEM tools report what they received, not what they missed. False negatives erode the detection coverage MSSPs guarantee to clients.
Tool licensing costs scale faster than revenue
SIEM platforms charge per gigabyte of ingested data. Without traffic conditioning, MSSPs feed redundant and irrelevant packets to expensive tools, inflating per-client operational costs. As client count grows, unfiltered traffic drives licensing spend that outpaces contract revenue.
Multi-client, multi-speed network complexity
MSSPs monitor client environments spanning 1G branch links to 100G data centre cores, often with mixed copper and fibre media. Each client network requires a separate visibility configuration, and SPAN's limited session count per switch forces compromises on which traffic gets monitored.
Compliance capture obligations across diverse frameworks
Clients in financial services, healthcare, and government require 100% packet capture for audit evidence under frameworks including PCI DSS, SOC 2, ISO 27001, and HIPAA. Sampled or incomplete capture from SPAN ports fails to satisfy these requirements, exposing the MSSP to contractual liability.

 Why managed security service providers come to Network Critical 

 We reduce SIEM and NDR ingestion costs by filtering irrelevant traffic before it reaches licensed tools. 

 We provide 100% packet capture with zero loss, so SOC teams detect threats with complete context. 

 We provide 100% packet capture with zero loss, so SOC teams detect threats with complete context. 

 We deliver tool-agnostic PCAP output that feeds any SIEM, NDR, or forensic platform your clients require. 

 We eliminate SPAN port contention, freeing switch resources for production workloads. 

 We automate traffic flows via API, enabling machine-driven SOC workflows that reduce mean time to detect. 

 Key capabilities for managed security service providers 

Intelligent traffic conditioning for SOC tool optimisation

Network Critical's SmartNA-PortPlus aggregates, filters, and load-balances traffic across your monitoring tool stack. Session-aware load balancing distributes client traffic by IP address, protocol, port, VLAN, or MAC address, ensuring each tool receives precisely the packets it needs. This reduces SIEM ingestion volumes and extends the operational life of existing security tools.

API-driven automation for managed SOC workflows

 The SmartNA-PortPlus integrated API enables SIEM and NDR platforms to control traffic flows programmatically, without human intervention. Darktrace demonstrated this capability by using the API to automatically adapt filtering and port mapping as its machine learning models identified new traffic patterns, eliminating manual reconfiguration cycles that slow incident response. 

Scale-out architecture for multi-client growth

 Starting at 48 ports in a single 1RU chassis, the SmartNA-PortPlus packet broker scales to 194 ports across five linked units. Each expansion unit connects to the base system and operates as a single managed fabric. New client environments are added by provisioning ports, not by replacing infrastructure. 

Zero-impact network access with passive TAPs

 Passive Fiber TAPs provide zero-power, zero-latency access to client network traffic without introducing any active device into the production path. For MSSPs deploying into client data centres and branch offices, passive TAPs eliminate the risk of impacting live services during installation and ongoing monitoring. 

 Best network visibility solution for managed security service providers 

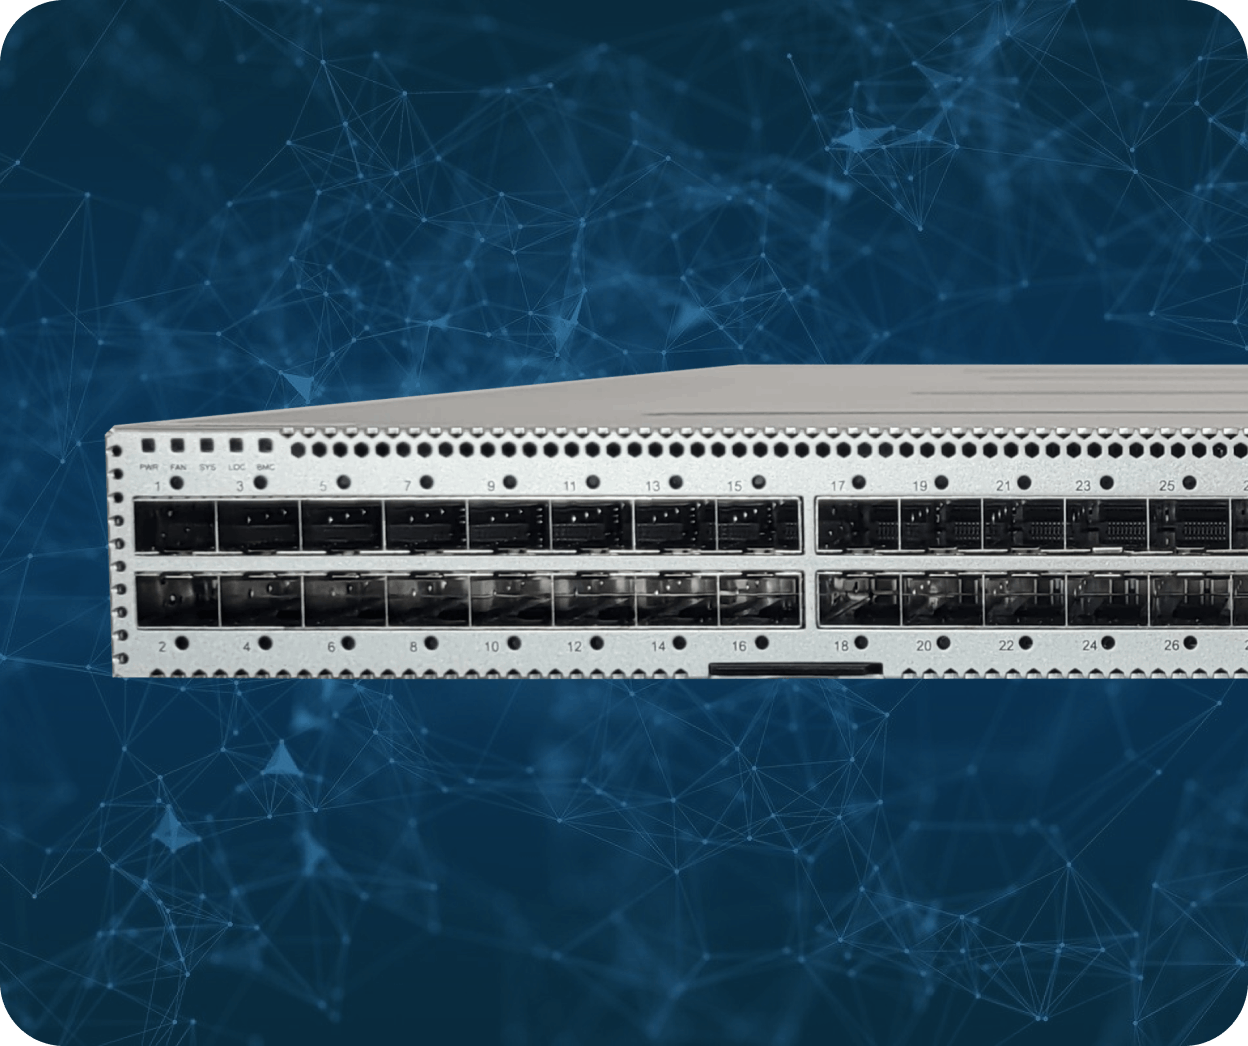
SmartNA-PortPlus scalable packet broker

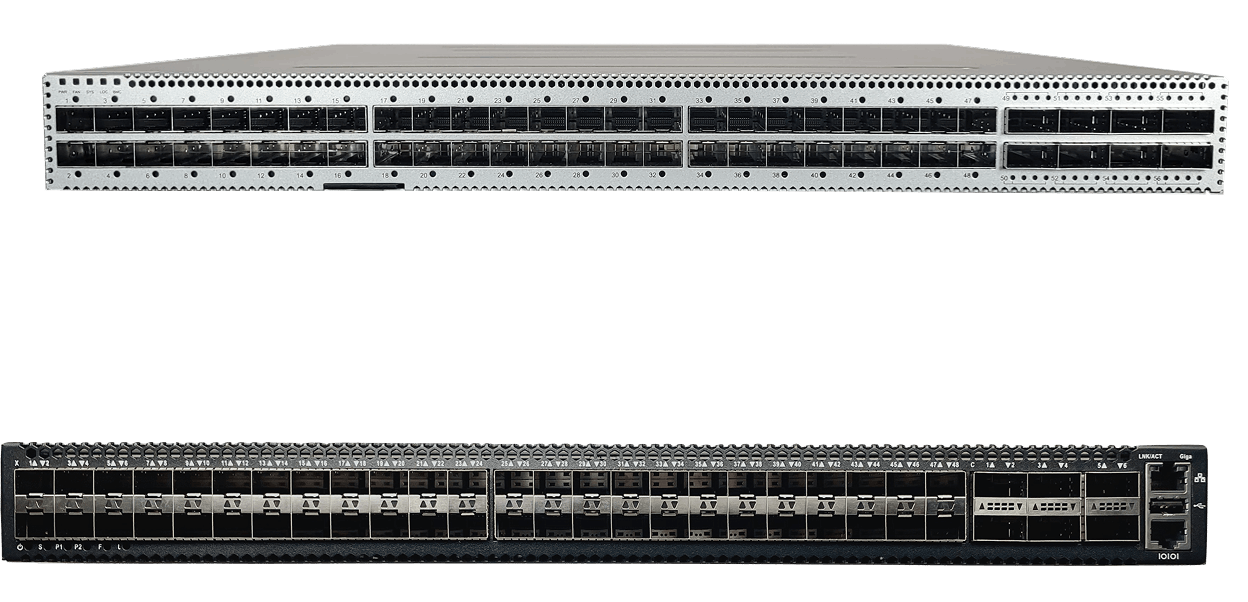
Network Critical's SmartNA-PortPlus is built for security operations that demand scale, flexibility, and tool-agnostic traffic delivery. Specifications as of 2026:

  • 48 x 1/10/25G SFP28 ports plus 8 x 40/100G QSFP ports per base unit
  • Non-blocking 1.8 Tbps line-rate throughput
  • Scalable from 1RU (48 ports) to 5RU (194 ports) as a single managed system
  • Aggregation, filtering, and session-aware load balancing by IP, protocol, port, VLAN, or MAC
  • Integrated API supporting HTTP and JSON for machine-to-machine automation
  • Drag-n-Vu graphical management for fast, error-free configuration
  • RADIUS and TACACS+ authentication, authorisation, and accounting
  • SNMPv3 integration with all major network management systems
  • Dual hot-swap power supplies for data centre resilience
  • Custom P-Tag functionality for complex traffic processing workflows
  • MTBF exceeding 582,692 hours
SmartNA-PortPlus on blue background
person typing on futuristic laptop

When SmartNA-PortPlus is the right fit

  • You're running SOC operations across multiple client environments and need a single visibility platform that scales by adding ports and modules, not by replacing infrastructure.
  • You need to reduce SIEM and NDR ingestion costs by conditioning traffic before it reaches licensed tools, filtering out irrelevant packets at the visibility layer.
  • You require API-driven automation for your SOC workflow, enabling security tools to control traffic flows programmatically as threat patterns evolve.
  • You operate across mixed-speed client networks spanning 1G to 100G and need a single system that handles copper, multi-mode fibre, and single-mode fibre simultaneously.

Case studies: network visibility in managed security operations

Darktrace integrated its AI-powered threat detection platform with Network Critical's SmartNA-PortPlus using the integrated API. The SmartNA-PortPlus automatically adapts filtering and port mapping as Darktrace's machine learning models identify new traffic patterns, creating a fully automated visibility and security architecture that detects threats in real time without manual reconfiguration. 

Read more

Vodafone deployed Network Critical SmartNA-XL hybrid TAPs and SmartNA-PortPlus packet brokers to achieve 100% accurate quality of service monitoring across four generations of network links. The deployment spans multiple link speeds and media types, delivering compliance-grade capture fidelity across a carrier-scale environment. 

Read more
Bourne leisure logo


 In a service business, the trust of our customers is paramount. We know that our customers are providing us with sensitive financial information every day. It is our responsibility to utilize the best technology available to protect that information from cyber criminals. Network Critical's solution allows us to connect the best security to our network without impacting reliability or availability of our network."

 —   CISO, Bourne Leisure 


 Why SPAN ports fail for managed security service providers 

Silent packet drops during client security incidents

SPAN is oversubscribed by design when multiple source ports feed a single destination at line rate. During DDoS events, anomaly spikes, or volumetric attacks, SPAN drops the packets your SOC needs most. No alarm fires when packets are lost. Your network packet brokers and network TAPs eliminate this risk by capturing every packet at full line rate, independent of switch CPU load.


Unscalable configuration across multi-client environments

 Most switches support only two to four concurrent SPAN sessions. For an MSSP monitoring dozens of client networks, SPAN requires configuring and maintaining sessions across hundreds of switches, each taking up to 45 minutes to configure correctly. Network Critical's modular architecture provisions new client environments by adding ports, not by touching switch configurations across the client estate. 

No compliance-grade audit trail for client obligations

SPAN's sampled, best-effort capture cannot satisfy PCI DSS, SOC 2, ISO 27001, or HIPAA audit requirements that demand 100% packet capture with verifiable completeness. When a client auditor requests evidence of continuous monitoring, SPAN's silent failure mode means the MSSP cannot prove what was or was not captured. Passive Fiber TAPs deliver deterministic, zero-loss capture that withstands audit scrutiny. Read more about network TAPs vs SPAN. 

Why choose Network Critical for network visibility for managed security service providers

Network Critical delivers the visibility infrastructure that lets MSSPs scale their SOC operations without scaling their costs. The SmartNA-PortPlus packet broker provides 48 to 194 ports of 1G to 100G access in a non-blocking, line-rate architecture, with the API-driven automation that modern security tools require to operate without manual intervention.

Unlike subscription-driven monitoring platforms, Network Critical's perpetual licensing model carries no per-port fees, no per-client surcharges, and no forced upgrade cycles. The Drag-n-Vu graphical interface enables SOC engineers to self-serve configuration changes in minutes, not hours. Typical deployments complete in under two hours, reducing client onboarding time and protecting service margins.

With over 20 years of network visibility experience and deployments across telecom, financial services, energy, and government, Network Critical provides a proven, tool-agnostic visibility architecture that works with any SIEM, NDR, or forensic capture platform. Organisations including Vodafone, Bourne Leisure, and Darktrace rely on Network Critical to protect their most critical traffic links.

 Frequently asked questions about network visibility for managed security service providers 

  • Network visibility for MSSPs is the ability to capture, aggregate, and deliver network traffic from multiple client environments to centralised SOC monitoring tools. Network Critical's packet brokers provide this capability at scale, filtering and load-balancing traffic so SIEM and NDR platforms receive precisely the data they need without packet loss. 

  • SPAN ports drop packets during high-traffic periods and support only two to four sessions per switch. For MSSPs monitoring multiple client networks, this creates detection blind spots and unscalable configuration overhead. Network TAPs capture 100% of traffic at line rate without contending for switch CPU resources. Read more about network TAPs vs SPAN. 

  •  The SmartNA-PortPlus filters irrelevant traffic before it reaches licensed SIEM tools, reducing per-gigabyte ingestion volumes. Session-aware load balancing distributes traffic across tools by IP, protocol, port, or VLAN, so each tool processes only the packets it needs. Documented deployments show up to 60% traffic reduction through intelligent conditioning. 
  • Yes. Network Critical delivers standard PCAP output compatible with any SIEM, NDR, APM, or capture platform, including Splunk, Microsoft Sentinel, Darktrace, ExtraHop, Corelight, Wireshark, and Endace. The SmartNA-PortPlus API integration with Darktrace demonstrates machine-to-machine automation for dynamic traffic control. 

  • The SmartNA-PortPlus integrated API uses standard HTTP and JSON protocols, allowing security tools to programmatically control filtering and port mapping without human intervention. Darktrace's deployment uses this API to automatically adapt traffic feeds as its machine learning models detect new patterns, eliminating manual reconfiguration during incident response. 

  • Typical Network Critical deployments complete in under two hours using the Drag-n-Vu graphical interface. New client environments are added by provisioning ports on existing infrastructure, not by reconfiguring switch SPAN sessions. The SmartNA-PortPlus scales from 48 to 194 ports without replacing the base unit. 
  • Network TAPs and packet brokers deliver 100% packet capture, satisfying audit requirements for PCI DSS, SOC 2, ISO 27001, HIPAA, and other frameworks that mandate continuous, verifiable network monitoring. Passive Fiber TAPs provide tamper-evident, zero-power access that strengthens compliance evidence. 

  • Bypass TAPs provide automatic failover when inline security tools (IPS, WAF, DDoS mitigation) experience failure or require maintenance. Traffic continues flowing through the network while the tool is serviced, ensuring client uptime is not affected by security tool outages. 
  •  Network Critical's perpetual licensing model delivers 40 to 60% lower three-year TCO compared to subscription-driven enterprise visibility platforms. There are no per-port licensing fees, no annual subscription renewals, and no forced upgrade cycles. For MSSPs, this predictable CAPEX model protects margins as client count grows. Talk to sales for a tailored TCO comparison. 
  •  The SmartNA-XL hybrid TAP connects copper, multi-mode fibre, and single-mode fibre links in a single 1RU chassis using hot-swappable modules. Bourne Leisure's deployment used this flexibility to aggregate eight mixed-media 1G links to a single 10G security tool, demonstrating the approach across a complex multi-site network. 

  •  A network TAP is a hardware device that creates a copy of live network traffic without impacting the production link. A network packet broker sits between TAPs and monitoring tools, aggregating, filtering, and distributing traffic to the right tools. MSSPs typically deploy both: TAPs for access and packet brokers for intelligent traffic management. Learn more about network packet capture. 
  •  Network Critical's product range covers 1G to 400G. The SmartNA-PortPlus handles 1G, 10G, 25G, 40G, and 100G in a single chassis. The SmartNA-PortPlus HyperCore extends coverage to 400G for MSSPs serving hyperscale data centre clients.