<img src="https://secure.leadforensics.com/97241.png" style="display:none;">

Network visibility for healthcare

Network Critical provides network visibility for healthcare providers running ransomware-targeted clinical networks, pairing invisible zero trust protection with zero-loss traffic capture on a healthcare budget.

Network teams at these organisations run Network Critical visibility

  • Vodafone Logo
  • HSBC Logo
  • bp logo
  • Airbus Logo
  • Darktrace Logo

Stopping ransomware inside the hospital network, without an enterprise security budget

Ransomware attacks rose sharply during the pandemic, and healthcare became a prime target as telemedicine and remote work widened the attack surface. Attackers know a hospital stretched by patient demand is under pressure to pay, and that unmanaged IoT and IoMT devices offer an easy way in. When one healthcare provider faced repeated threats, its CISO placed INVIKTUS in front of server-based patient data storage. The servers became invisible to unauthorised users, compromised devices were quarantined, and the project stayed within budget. Add SmartNA-XL TAPs feeding your detection tools, and you get network visibility for healthcare that catches what SPAN drops and blocks what slips through.
Key challenges facing healthcare providers

Ransomware that targets patient care
Attackers time ransomware for maximum pressure, knowing a cyberattack can delay care, cancel procedures, and put lives at risk. Network Critical's INVIKTUS places an invisible zero trust layer in front of critical servers, so attackers moving through the network never find the systems that matter.
Unmanaged IoT and IoMT devices
Video cameras, HVAC controllers, and connected medical devices support patient care, but they rarely run security agents. Malware uses them to explore the network from inside. Network Critical's SmartNA-XL copies traffic from those segments to your detection tools, so unmanaged devices stop being blind spots.
Security budgets that cannot keep pace
Healthcare organisations often lack the funds for enterprise security platforms, yet carry the same duty to protect patient records. Network Critical's Passive Fiber TAPs need no power and no configuration, and carry zero ongoing maintenance costs, giving you permanent capture on critical links.
Lateral movement nobody sees
Perimeter tools watch traffic entering and leaving the network, not traffic moving between internal systems. That is where ransomware spreads before it detonates. Network Critical's network packet brokers aggregate east-west links and deliver internal traffic to your security tools at full fidelity.

Why healthcare IT teams come to Network Critical

We watched ransomware hit a peer hospital, and our board wants a plan.

We must protect patient data servers but can't fund another enterprise security platform.

We're connecting medical IoT devices faster than our security team can verify them.

We have a HIPAA audit coming and need proof our monitoring is complete.

We're expanding telehealth and remote access, and our attack surface keeps growing.

We suspect SPAN is dropping packets before they ever reach our detection tools.

Key capabilities for healthcare providers

Invisible zero trust protection for critical servers

Network Critical's INVIKTUS has no IP or MAC address, so attackers scanning your network can't see it or the servers behind it. Every user, application, and device must be validated before it reaches patient data. 

Lock and Leave for lean IT teams

 Program your access policies once, lock them, and let INVIKTUS run in the background at full line rate with minimal maintenance. Each user gets one approved path, and the rest of the network stays invisible to them. 

Full-fidelity traffic for your detection tools

 Network Critical's SmartNA-XL aggregates copper and fibre links into your security tools. PacketPro payload masking hides sensitive content before it reaches a tool, and the Drag-n-Vu interface makes configuration fast and error-free. 

Always-on capture for compliance links

 Network Critical's Passive Fiber TAPs keep capturing traffic during a power outage, with insertion loss as low as 1.3dB and no configuration. Their one-way design stops data flowing back into the network, so the monitoring point can't become an attack path. 

Best network visibility for healthcare providers

INVIKTUS

  • Zero trust "Trust No-one" model that validates every user, application, and device, inside or outside the network
  • No IP or MAC address, so it stays invisible to anyone scanning the network
  • Full line-rate performance with zero latency
  • Policy-based configuration that maps one approved path per user and hides everything else
  • Lock and Leave operation: program the policies, lock them, and let it run with minimal maintenance
  • Continuously blocks unauthorised users and supports quarantine of compromised devices
  • Deploys in front of the critical servers that hold patient and personal data
  • Positioned as affordable for any budget and network size
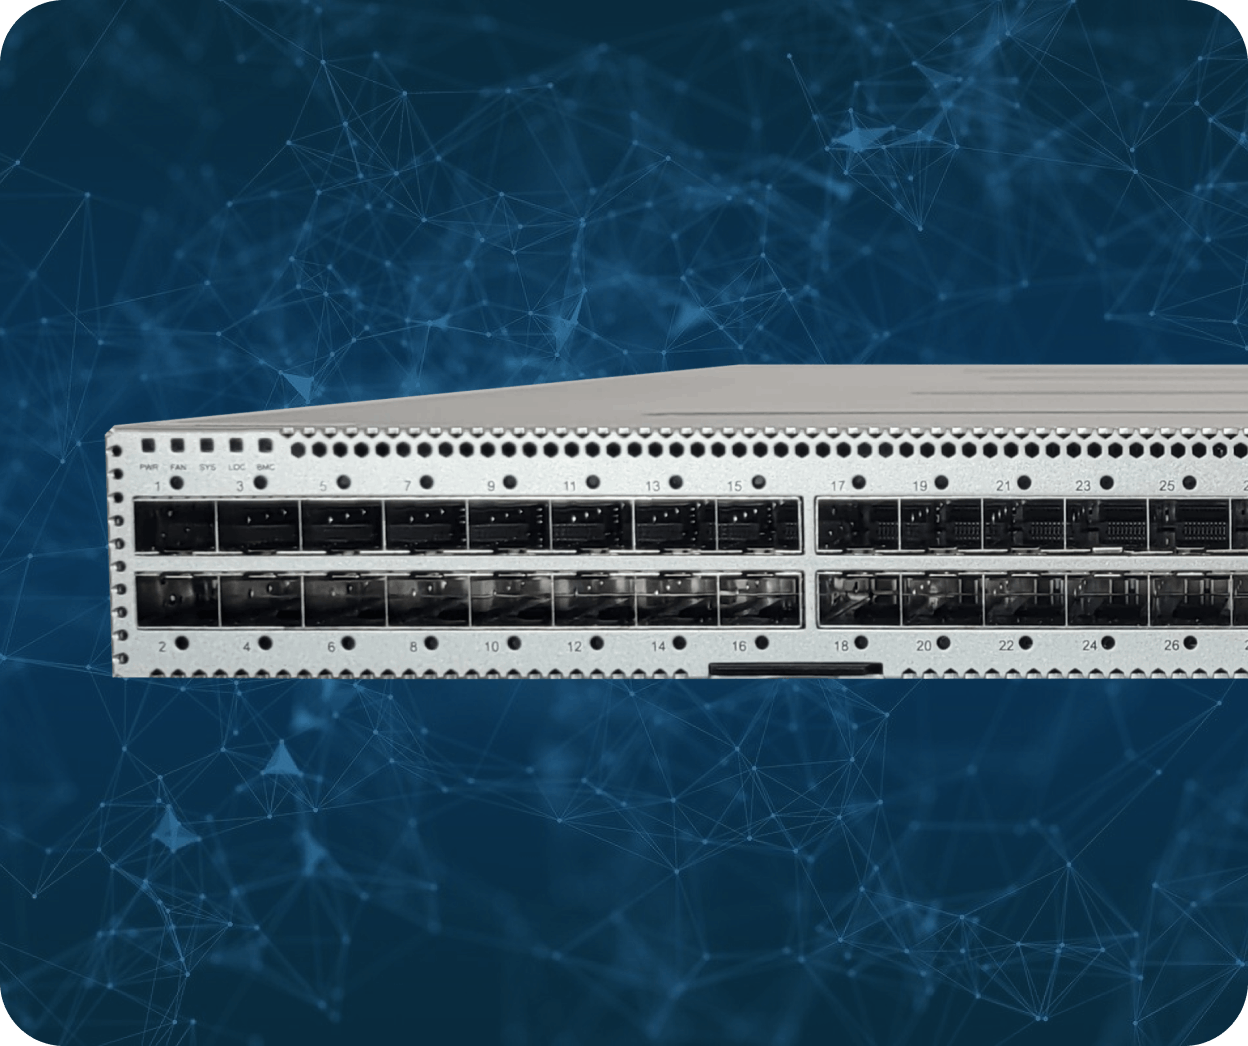
SmartNA-PortPlus on blue background
person typing on futuristic laptop

When INVIKTUS is the right fit

  • You need to protect patient data servers from threats that are already inside the network.
  • You're connecting IoT and IoMT devices that you can't patch or fully manage.
  • You want a zero trust security layer but can't fund an enterprise security platform.
  • Your IT team needs protection that runs with minimal maintenance once policies are set.

Case studies: network visibility for healthcare in hospitals and beyond

After repeated ransomware threats, a hospital CISO worked with Network Critical to place INVIKTUS in front of new server-based patient data storage. The organisation now prevents cyber threats, detects illicit ERP access attempts, and quarantines compromised devices, all within budget, while sensitive data stays invisible to unauthorised users.


We needed to upgrade our network security but could not afford a very expensive solution, INVIKTUS provided us with a very strong security at a fraction of the cost. Now our critical servers are protected from security breaches from within the network." 

 —   Network Manager, Hospital 


Why SPAN ports fail for healthcare providers

SPAN drops packets when ransomware moves

SPAN is oversubscribed by design, so it drops packets during traffic spikes, exactly when ransomware spreads between clinical systems. No alarm fires, and your tools only report what SPAN sent them. A dedicated network TAP copies every packet, every time. 

SPAN can't reach every clinical segment

 Most switches support only two to four SPAN sessions, so medical device, guest, and server segments compete for a handful of mirror ports. Whatever misses out goes unmonitored. SmartNA-XL aggregation puts every critical link in front of your tools. 

SPAN can't give auditors complete evidence

Dropped packets leave gaps in forensic records, which makes evidence for HIPAA audits and incident investigations hard to defend. Passive fiber TAPs capture the full stream with no power dependency, so your records hold up when someone asks what happened. 

Why choose Network Critical for network visibility for healthcare

Healthcare security budgets rarely stretch to enterprise visibility platforms or subscription-driven monitoring stacks. INVIKTUS gives you zero trust protection sized for any budget and network size, and Network Critical visibility hardware is sold on perpetual licences, so costs don't climb at every renewal.

The tools you already own get more value too. Bourne Leisure protects eight live links with one security tool through SmartNA-XL. Darktrace automates filtering and port mapping on SmartNA-PortPlus through its API, and the State of Maryland relies on SmartNA-XL for unified communications monitoring.

Add Passive Fiber TAPs where power and maintenance windows are scarce, and you have a security layer that runs quietly while your team keeps clinical systems online. With more than 20 years in network access technology, Network Critical already protects networks across finance, telecoms, government, energy, and healthcare.

Frequently asked questions about network visibility for healthcare

  •  It means seeing every packet that moves across clinical, administrative, and device networks, so security tools can spot threats early. Network Critical delivers it through TAPs and packet brokers that copy traffic without loss, alongside network security monitoring solutions and INVIKTUS to protect critical servers. 

  •  INVIKTUS sits in front of critical servers and applies a zero trust policy: no user, application, or device gets through until it's validated. Because it has no IP or MAC address, ransomware moving laterally through the network can't see the servers it's hunting for. 

  •  In a zero trust architecture, a newly connected device can't reach protected systems until it's verified and granted access. The healthcare provider in our case study used INVIKTUS zero trust to quarantine compromised devices and detect illicit ERP access attempts, without exceeding its budget. 
  • INVIKTUS is positioned as affordable for any budget and network size. A hospital network manager said INVIKTUS gave them very strong security at a fraction of the cost of the expensive alternatives. Talk to sales for pricing based on your network. 

  • Very little. With Lock and Leave, your team programs the access policies, locks them, and leaves the INVIKTUS zero trust layer running in the background. That suits healthcare IT teams who can't spend hours tuning another security tool every week. 

  • SPAN drops packets under load without raising an alarm, and most switches support only two to four sessions. That leaves gaps exactly when ransomware is spreading. Our comparison of network TAPs vs SPAN sets out the differences in full. 
  • A network test access point (TAP) connects to your cabling and copies send and receive traffic on separate channels to your monitoring tools in real time. It doesn't compete with switching workload the way SPAN does. Our explainer on what is a network tap covers the basics. 

  • SmartNA-XL is a key enabler for regulations including HIPAA, SOX, and PCI-DSS. PacketPro payload masking hides sensitive content before traffic reaches a tool, and lossless capture gives auditors evidence that monitoring covers your critical systems. 
  • Yes. Aggregation lets one tool cover many links. Bourne Leisure connects eight live 1Gbps links to a single 10Gbps security tool through SmartNA-XL, an 8:1 configuration that cut security tool CAPEX eightfold. Hospitals can apply the same approach to their detection tools. 
  • No. Passive Fiber TAPs keep capturing traffic during a power outage. They need no configuration, carry zero ongoing maintenance costs, and fit up to 16 TAPs in 1RU for 1G and 10G links, with MPO options for 40G and 100G. 

  • Bypass TAPs send continuous heartbeat signals to inline appliances. If a tool stops responding, traffic reroutes automatically, so clinical systems stay online while you fix or update the tool. Dual hot-swappable power supplies add further resilience. 
  • Drag-n-Vu gives you one web interface to set up aggregation, filtering, load balancing, and port mapping by drag and drop. Its dashboard shows key performance indicators at a glance, and configuration is fast and error-free, so a small team can run the platform.